What does a VPN protect—and where does it stop?
A protected connection has an endpoint.
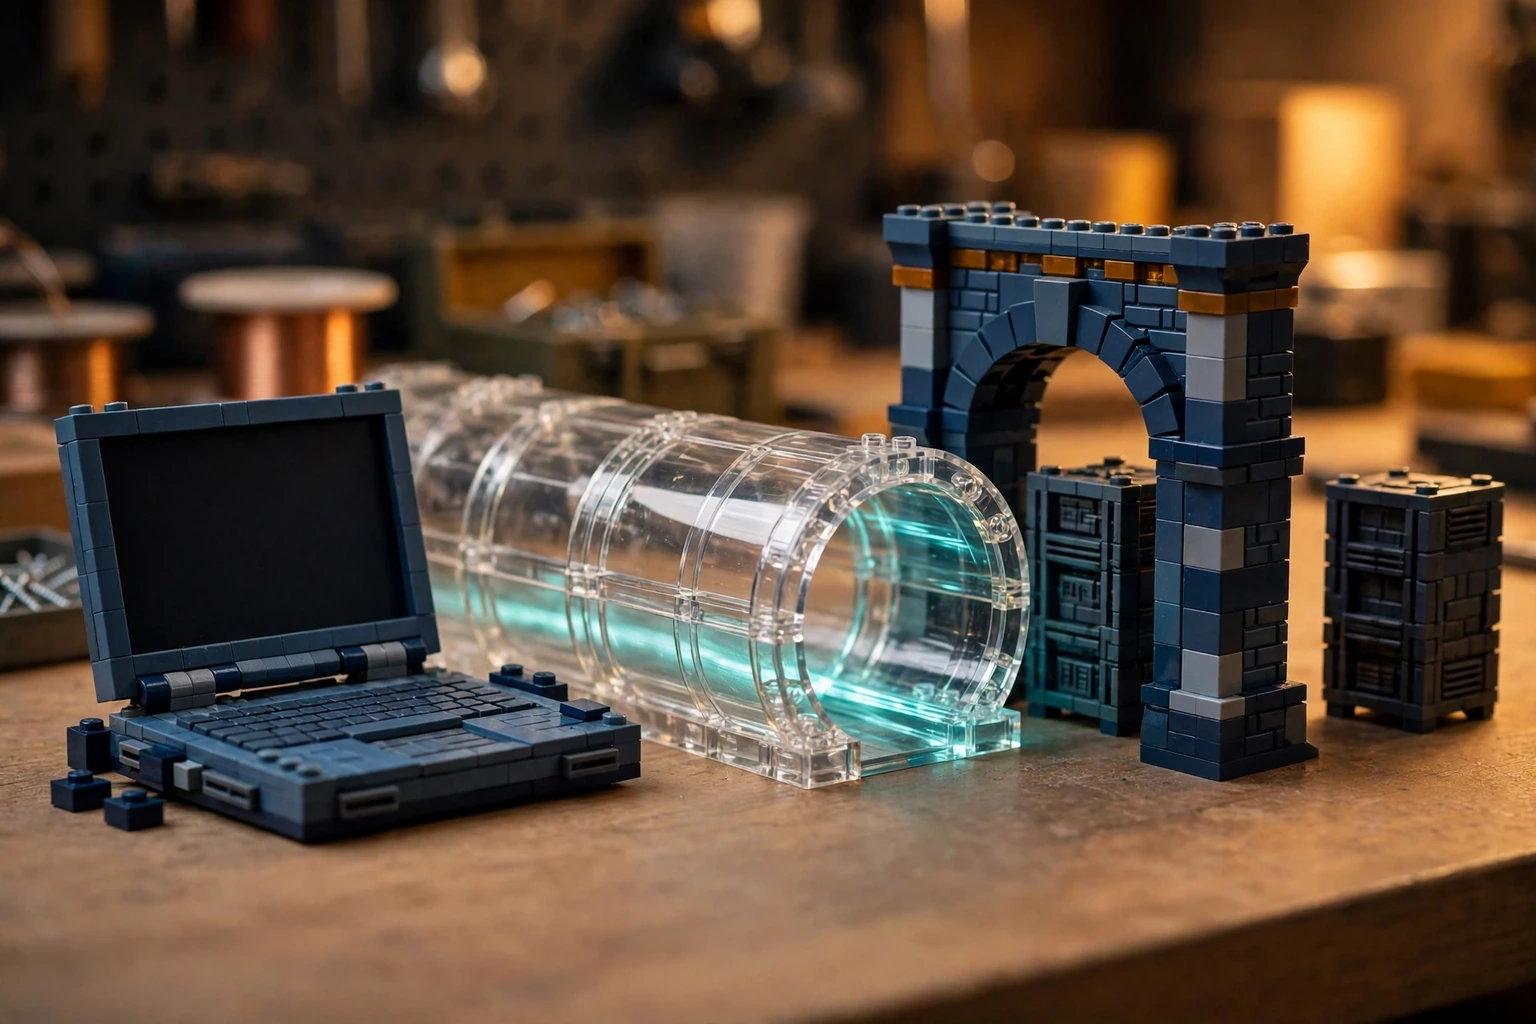
The tunnel has an endpoint.
VPN / one protected leg does not describe the whole journey.
Follow the idea
- The device establishes a VPN connection to the gateway.
- Only traffic routed into that tunnel uses this protected leg.
- The VPN leg ends at the gateway; the next connection needs its own protections.
Keep the limit visible
Illustrative remote-access VPN. A VPN does not repair a compromised endpoint or automatically make a user anonymous.
Where does this VPN’s encrypted leg end?
At the VPN gateway shown here. HTTPS/TLS and the application’s permission checks are separate protections.
“Connected to a VPN means every part of the journey is protected.”
Identify the endpoint, which routes enter the tunnel and the controls on the next leg.Source for this graphic: www.cloudflare.com ↗ · Checked November 7, 2026 · Illustrative example.
Start with the tunnel
A virtual private network creates an encrypted connection between endpoints. A common enterprise example connects a remote device to a company access point so work traffic can travel through that tunnel.
Follow one request
Illustrative example: a remote worker connects to a company VPN gateway before opening a private application. The tunnel and the application’s own permission checks solve different problems.
Keep the boundary visible
A VPN does not make every activity anonymous or make a compromised device safe. What happens beyond its endpoint, which traffic enters the tunnel and who operates it all matter.
The next smart question
Where does the tunnel end, and what happens to the traffic after that?
Independent explanation. No sponsorship or endorsement implied. Product features and policies can change; check the exact product and configuration.
Published .